Next.js 16.4 shipped on October 6, 2026, and it quietly changed the advice for every team running the App Router. In the release post , the Next.js team now recommends Cache Components as "the best choice for every Next.js app," turns it on by default for new projects created with create-next-app , and states plainly that it will become the default in Next.js 17. No date has been announced for 17 — but the direction is set. If you are a founder with a SaaS dashboard, marketing site, or customer portal on Next.js, this is not a reason to panic-refactor. It is a reason to put the migration on the roadmap deliberately, before a major-version upgrade forces the decision for you. Here is how we would plan it.
What Next.js 16.4 Cache Components actually change
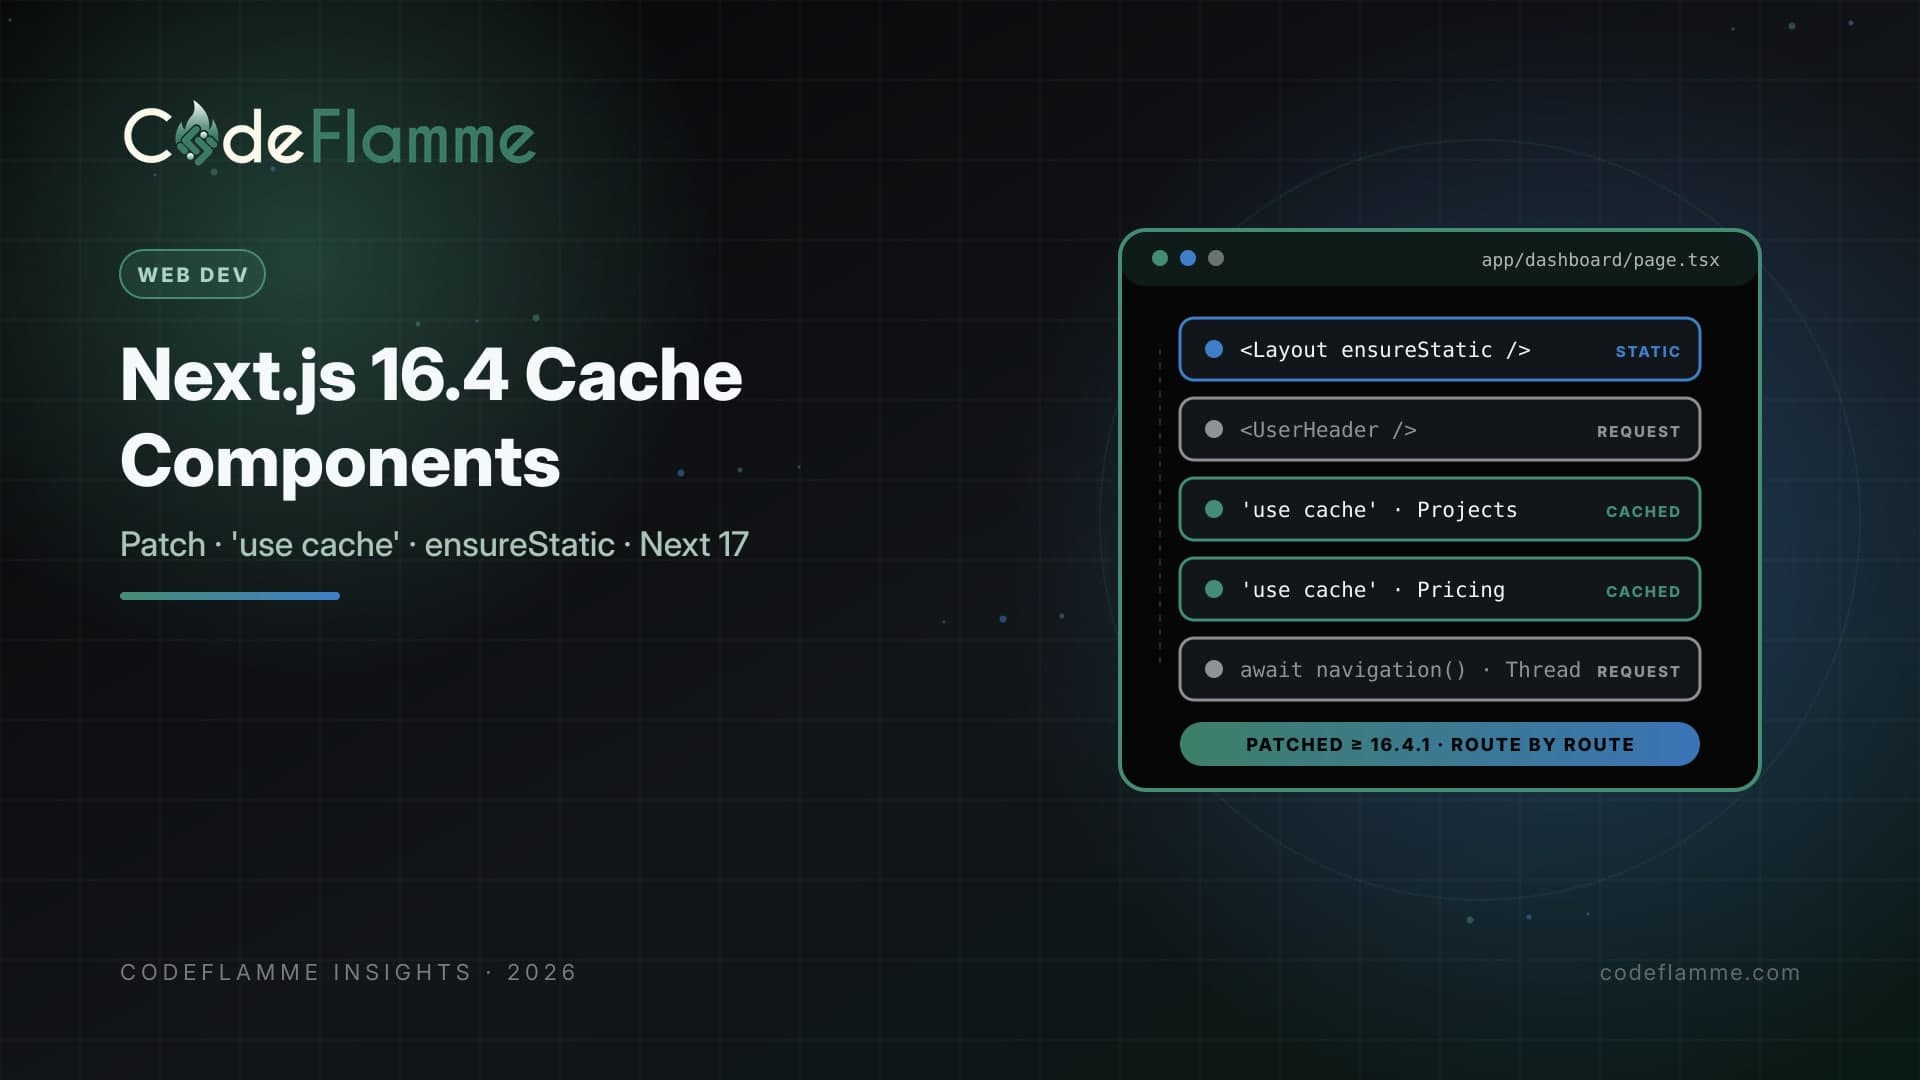
Cache Components replace the implicit caching behaviour of earlier App Router versions with explicit, opt-in annotations. The 'use cache' directive works like a component-level Cache-Control header: you mark which parts of a page can be cached, and everything else renders at request time. Next.js caches that UI in the browser for client navigations and, optionally, on the server or at build time. In practice the model is two flags in next.config.ts — cacheComponents and partialPrefetching — and the release post says Partial Prefetching is now considered part of the model. For a typical B2B SaaS screen, that means a personalised header (current user, workspace) can stream alongside a cached project list in a single response, instead of the whole page being forced dynamic because one component reads a cookie.
// next.config.ts — the two flags the 16.4 release post describes
import type { NextConfig } from 'next';

const nextConfig: NextConfig = {
  cacheComponents: true,
  partialPrefetching: true,
};

export default nextConfig;
Why founders should care: cost, speed, and fewer caching surprises
The old implicit model is where many of the caching bugs we see in rescue projects come from: a page that was meant to be personalised gets cached, or a page meant to be static goes dynamic and quietly multiplies server cost. Explicit annotations make the intent reviewable in a pull request. That matters when an agency or a new hire touches the codebase six months from now. Next.js 16.4 also adds ensureStatic , which fails the build if dynamic content sneaks into a route you meant to keep static. You can set it to 'navigation' , 'prefetch' , or 'shell' , per page or per layout. For marketing pages, docs, and blog routes — the pages that carry your SEO — that is a cheap guardrail against an accidental request-time render. (If your marketing site is still a client-only SPA, start with why client-only SPAs fail search first.) For data-heavy screens, the new navigation() and prefetch() APIs let you defer expensive parts of a page until the user actually navigates, so a list of prefetched links does not load every detail view in advance. That is a direct lever on database load for inbox-, ticket-, or record-style SaaS UIs.
A migration plan that will not break production
1. Get onto the 16.x line and patch. If you are still on Next.js 15, its Maintenance LTS window ends on October 21, 2026 — we covered the patch floor and Active LTS path separately. Cache Components is a 16.x story; do the version upgrade as its own release, with no behaviour changes mixed in. 2. Use the new agent tooling, but review its output like a junior PR. 16.4 adds next upgrade --agent , which prepares migration guides, codemods, and verification steps for a coding agent, plus Skills for adopting Cache Components and Partial Prefetching. That is useful for mechanical changes. It is not a substitute for someone who knows which of your pages are tenant-specific. 3. Inventory routes by data sensitivity before you add 'use cache' . In multi-tenant SaaS, the expensive mistake is caching something keyed too broadly. For every cached function, write down what it is keyed on (user, workspace, plan) and how it is invalidated. If nobody can answer that, leave it dynamic for now. 4. Lock static routes with ensureStatic . Start with marketing, pricing, and docs layouts. A failed build is far cheaper than a pricing page that silently renders per request. 5. Measure before and after. Track server function invocations, time to first byte, and navigation latency on your top routes for a week before and after. Keep the rollout per route or per layout so you can revert one area without reverting the release.
// app/(marketing)/layout.tsx — fail the build if a dynamic component slips in
export const ensureStatic = 'navigation';

export default function MarketingLayout({ children }) {
  return <>{children}</>;
}
What you get for free just by upgrading
Even without touching Cache Components, 16.4 brings improvements every app gets: Turbopack's disk cache uses 20–25% less space, server HMR is lazy, Turbopack ships a shared runtime chunk, production CSS class names and export names are shorter, and React 19.3 arrives with stable View Transitions and Fragment Refs. Those are good reasons to schedule the upgrade even if the caching migration waits a quarter. There are also experimental options — a Rust build of the React Compiler, Turbopack garbage collection, lazy dynamic imports, worker threads — that we would keep out of production until they leave the experimental channel. Note the release post's own caveat: on Node.js 24.13.1 and newer, the worker-threads option currently falls back to child processes because of a Node.js bug.
The founder checklist
Ask your team or agency five questions this sprint: Are we on a patched 16.x release? Which routes must stay static, and are they guarded with ensureStatic ? What is every cached function keyed on? Who reviews agent-generated upgrade changes? What metrics will tell us the migration helped? If those answers are vague, that is normal — most App Router codebases grew their caching by accident. The fix is a short audit, not a rewrite. When a codebase has drifted far enough that the audit turns into archaeology, our rescue playbook on rebuild vs stabilize is the next read.